Three small DNS records stand between your cold emails and the spam folder.
SPF, DKIM and DMARC explained simply: they are the three checks that let a receiving inbox prove an email really came from your domain, and not from someone pretending to be you. Every serious cold email sender needs all three, because Gmail and Yahoo now expect them from bulk senders, and because an inbox that cannot verify you has every reason to distrust you. This guide explains each check in plain English first, then in full technical detail, with the exact DNS records to publish, the common errors, and the tools that watch your setup for you.
Visit Postmark →Explore Mailgun →See Do You Mail →All tool prices in this guide were checked on 16 November 2026 on the providers’ official sites. Features and pricing can change, so please check the provider’s site before you buy. We do not guess at features, prices or trials.
Quick Answer
SPF, DKIM and DMARC explained in one paragraph: SPF is a DNS list of the servers allowed to send email for your domain, DKIM is a cryptographic signature that proves an email was not changed on the way, and DMARC is the policy that tells receiving inboxes what to do when SPF or DKIM fails, plus the reports that show you who is sending as you. Set up SPF first, then DKIM, then DMARC at p=none so you can read the reports, and move to p=quarantine and then p=reject only once your own mail passes cleanly.
One warning matters more than any other in this guide: never jump straight to p=reject. For example, a strict policy published before your own sending is fixed will block your own real emails. In fact, the safe path takes about two weeks of watching reports at p=none, then quarantine, then reject. That patience is the difference between authentication that protects you and authentication that silences you.
Contents
- What SPF, DKIM and DMARC are, in plain English
- How the three checks work together
- SPF in depth: the approved-sender list
- DKIM in depth: the wax seal on every email
- DMARC in depth: the policy and the reports
- Setting up SPF, DKIM and DMARC, step by step
- Common errors and how to fix them
- How to check your setup
- BIMI in brief: your logo in the inbox
- Tools that help with SPF, DKIM and DMARC
- Who should do what: the decision framework
- Frequently asked questions
- The verdict
Authentication is the foundation every other deliverability habit sits on
Firstly, email was built without any proof of identity, and that is the root of the whole problem. For instance, anyone can send an email that claims to come from your domain, because the original email protocol never asked the sender to prove who they were. Similarly, a spammer can put your name in the From line, and the receiving inbox has no way of knowing the difference on its own. In short, SPF, DKIM and DMARC are the three answers the industry built to fix that gap, one layer at a time. That is why this guide treats them as one system, not three separate chores.
Secondly, the stakes are practical, not theoretical. In fact, Gmail and Yahoo now require SPF, DKIM and DMARC from senders who send bulk email to their users, and they watch spam complaint rates closely. For example, a sender with no DMARC record at all will see warnings from inbox providers, and a sender whose records are broken will see mail land in spam or bounce. Moreover, a sender whose domain is spoofed by criminals will watch their reputation fall for emails they never sent. As a result, authentication is not a nice extra for a cold email sender. It is the price of entry.
What this guide checks, and how
Every price in this guide comes from the provider’s own website, checked on 16 November 2026. The DNS examples use example.com, a domain reserved for documentation, so nothing here points at a real customer. Where a provider does not show a price for a feature, this guide says so plainly rather than guessing. For the sending-domain side of the story, see our How to Set Up a Sending Domain 2026 guide, and for the warmup side, see our How to Warm Up a New Email Domain 2026 guide.
What SPF, DKIM and DMARC are, in plain English
In fact, the simplest way to understand the three checks is a parcel delivery. For example, SPF is the list of couriers allowed to deliver parcels from your address. In contrast, DKIM is the wax seal on the parcel that proves nobody opened it on the way. In short, DMARC is the instruction card on the door that tells the doorman what to do with a parcel that has no courier on the list or a broken seal, and asks the doorman to send you a note about it. A parcel needs all three to be trusted: an approved courier, an unbroken seal, and a clear instruction.
Moreover, each check answers a different question. In fact, SPF answers “is this server allowed to send for this domain?” Similarly, DKIM answers “is this email exactly as the sender wrote it?” As a result, DMARC answers “what should the inbox do when those two answers are no, and how do I find out about it?” A sender who understands those three questions understands the whole system, and the technical detail later in this guide is just the exact wording of each answer.
SPF DKIM DMARC explained: the three checks at a glance
| Check | What it proves | Where it lives | What it stops |
|---|---|---|---|
| SPF | The sending server is allowed to send for your domain | A TXT record on your domain | Servers that are not yours sending as you |
| DKIM | The email was not changed after the sender signed it | A TXT record under a selector, plus a signature in each email | Tampering and forged content |
| DMARC | SPF or DKIM lines up with the From address, and what to do if not | A TXT record at _dmarc.yourdomain | Spoofing of the address your readers actually see |
The table above is the plain-English summary of the three checks. The technical sections that follow give the exact record syntax for each one. Last checked: 16 November 2026.
Why one check alone is never enough
Secondly, each check has a blind spot that only the others cover. In fact, SPF checks the envelope sender, which is the address the reader never sees, so a spammer can pass SPF with their own domain while forging your name in the visible From line. Similarly, DKIM proves an email was not changed, yet it says nothing about what the inbox should do when the signature is missing. Moreover, DMARC on its own does nothing at all, because it has no check of its own: it only builds on SPF and DKIM results. In sum, the three checks are a team, and a sender who publishes only one of them has built one leg of a three-legged stool.
In addition, the blind spots explain the order of the work. Above all, SPF comes first because it is the simplest record to publish and the easiest to test. For example, DKIM comes second because it needs a key pair and a selector, which most sending tools generate for you. Similarly, DMARC comes last because it needs both of the others working before its policy means anything. As a result, a sender who follows that order, SPF, then DKIM, then DMARC at p=none, will have a working system in an afternoon, and a safe one in about two weeks.
How the three checks work together
In fact, the three checks run in sequence every time an email arrives. For example, the receiving server looks up the SPF record for the envelope sender’s domain and checks whether the sending server’s address is on the list. Similarly, it reads the DKIM signature in the email header, fetches the public key from DNS, and checks whether the signature matches the message. Moreover, DMARC then looks at the visible From address, asks whether the SPF result or the DKIM result lines up with that address, and applies the policy when neither does. That sequence, SPF, then DKIM, then DMARC, is the whole journey of every email you send.
Secondly, the key word in that sequence is alignment. In fact, DMARC does not ask whether SPF or DKIM passed in general. For example, it asks whether they passed for the same domain the reader sees in the From line. Similarly, a third-party tool that sends from its own domain can pass SPF and DKIM perfectly, yet still fail DMARC for your domain, because neither result lines up with your From address. As a result, alignment is the idea that turns three separate checks into one system, and the next section explains it in full.
SPF DKIM DMARC explained: what alignment means
Alignment means the domain that passed the check matches the domain in the visible From address. Firstly, SPF alignment compares the envelope sender domain, the Return-Path, with the From domain. For instance, an email sent from mail.example.com with a From address at example.com aligns under relaxed alignment, because both share the organisational domain example.com. Similarly, DKIM alignment compares the d= domain in the signature with the From domain, and the same relaxed rule applies. That test is what stops a spammer from passing the checks with a domain they control while showing your name to the reader.
Strict alignment works differently, and it is tighter. Under strict rules, the envelope sender domain must match the From domain exactly, not just share an organisational domain. For example, mail.example.com would fail strict alignment against a From address at example.com, while example.com itself would pass. Similarly, strict DKIM alignment requires the d= value to match the From domain character for character. Moreover, relaxed alignment is the default, and it suits almost every cold email sender, because sending tools normally use a subdomain for the envelope sender. As a result, keep relaxed alignment unless you have a specific reason to tighten it, and set it with aspf=r and adkim=r in the DMARC record.
The pass and fail logic, in one table
| SPF result | DKIM result | DMARC result | What the inbox does |
|---|---|---|---|
| Aligned pass | Anything | Pass | Delivers normally |
| Fail | Aligned pass | Pass | Delivers normally |
| Fail | Fail | Fail | Applies your DMARC policy |
| Pass, not aligned | Pass, not aligned | Fail | Applies your DMARC policy |
The logic above is the heart of DMARC: only ONE aligned pass is needed, from either SPF or DKIM. That is why DKIM matters so much for cold email, because forwarding breaks SPF while DKIM usually survives. Last checked: 16 November 2026.
Why forwarding breaks SPF and usually spares DKIM
Forwarding is the classic reason SPF fails on real mail. Firstly, a forwarded email arrives from the forwarder’s server, not the original sender’s server, so the forwarder’s address is not on the original SPF list. For example, a prospect who forwards your email to a colleague will see SPF fail on the forwarded copy. Similarly, a mailing list that resends your email has the same problem. Moreover, DMARC was built with this in mind: if DKIM still passes and aligns, DMARC passes anyway, and the email is delivered. As a result, DKIM is the safety net that keeps forwarding from breaking your deliverability, which is one more reason to set it up carefully.
In addition, that safety net has limits. Above all, a forwarder that changes the email content, for example by adding a footer, will break the DKIM signature too, because the signed body no longer matches. For instance, some mailing lists add a footer to every message, and those messages will fail both checks. Similarly, a DMARC policy of p=reject will then block them outright. In sum, the practical lesson is simple: make DKIM strong, keep your DMARC policy gentle until the reports show clean passes, and never assume forwarding is harmless.
How the three checks look together, on video
Video: SPF, DKIM and DMARC: how they work together by PeelSec on YouTube. This video is the creator’s property, embedded via YouTube for education. OutreachCompare is not affiliated with PeelSec and does not claim ownership of this video.
In fact, the video above is the clearest walk-through of the whole system in this guide. For instance, PeelSec follows a fake email through all three checks, shows why an email can pass SPF and DKIM yet still fail DMARC, and demonstrates the fix live in a small lab. It also covers the p=none to quarantine to reject progression, what DMARC reports show, and what DMARC cannot stop, such as look-alike domains. Watch it before you touch your DNS records: ten minutes here will save hours of guessing later.
SPF in depth: the approved-sender list
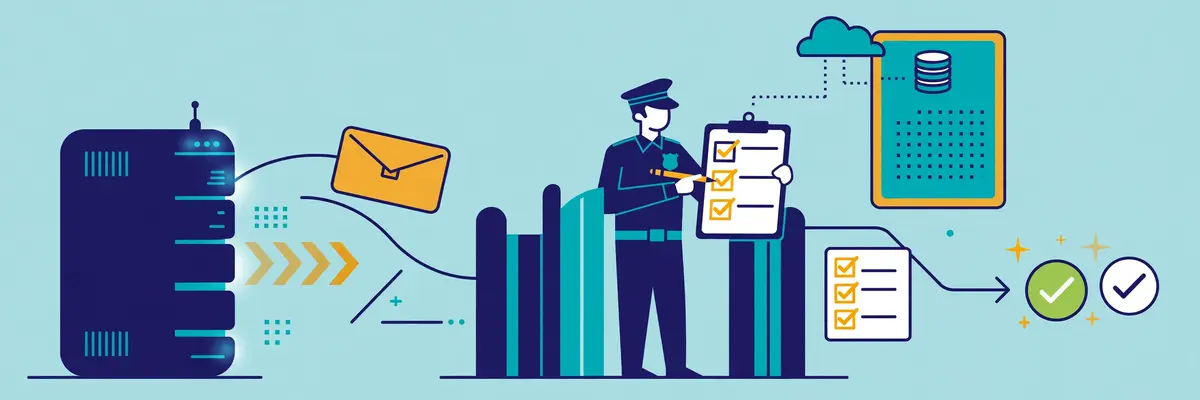
In fact, SPF, Sender Policy Framework, is a single TXT record on your domain that lists every server allowed to send email for it. For example, when an email arrives, the receiving server reads the envelope sender, looks up that domain’s SPF record, and checks whether the sending server’s IP address is on the list. Similarly, a server on the list passes, and a server off the list fails. In short, SPF is a guest list, and any server not on it is turned away.
Secondly, SPF has one detail that trips up many senders: it checks the envelope sender, not the address the reader sees. In fact, every email has two senders, the envelope address in the Return-Path header, which the reader never sees, and the visible From address. For example, a sending tool normally uses a subdomain such as mail.example.com as the envelope sender, while the reader sees hello@example.com. Moreover, that split is exactly why DMARC alignment exists, and why SPF alone cannot stop spoofing of the visible From line. As a result, SPF is the first layer, never the whole defence.
SPF DKIM DMARC explained: reading an SPF record
An SPF record is one line of text, and every part of it means something. The record below is a realistic example for a sender using Google Workspace and a cold email tool, with the example domain standing in for your own. Read it left to right: the version tag, then one mechanism after another, then the final rule that decides what happens to everything else.
v=spf1 ip4:192.0.2.10 include:_spf.google.com include:mail.example.com -allIn fact, v=spf1 marks the record as SPF version one, and it must come first. For example, ip4:192.0.2.10 allows one specific server by its address, while include:_spf.google.com pulls in Google’s own list of sending servers. Similarly, include:mail.example.com pulls in the cold email tool’s list, and -all at the end says every other server fails. Moreover, the qualifier before all decides the failure: -all means hard fail, ~all means soft fail, and +all would allow the whole internet, which is a serious mistake. As a result, -all is the right ending for almost every sender, once the record is tested.
The SPF mechanisms, and when to use each one
| Mechanism | What it does | Use it when |
|---|---|---|
| ip4 / ip6 | Allows one address or range | You send from a fixed server, such as Do You Mail |
| include: | Pulls in another domain’s SPF record | A tool publishes its own SPF, such as Google or your sender |
| a / mx | Allows your domain’s web or mail server | Your own server sends mail directly |
| -all | Everything else fails | Your list is complete and tested |
| ~all | Everything else soft-fails | You are still testing, or unsure the list is complete |
The mechanisms above cover almost every SPF record a cold email sender will write. Start with ~all while you test, then switch to -all once your own mail passes cleanly. Last checked: 16 November 2026.
SPF DKIM DMARC explained: the 10-lookup limit
SPF has a hard limit that catches out senders who add tool after tool. Firstly, an SPF check may trigger at most ten DNS lookups, and every include, a, mx, ptr and exists mechanism counts toward that limit, while plain ip4 and ip6 entries do not. For instance, a record with six includes, each of which pulls in two more, can blow past ten lookups before the check finishes. Similarly, the receiving server then returns a permerror, a permanent error, and the SPF check fails. As a result, the sender who keeps adding includes without counting will break their own authentication.
In addition, the fix is usually simple. Above all, count your lookups with a free SPF checker before you publish, and flatten the record when the count gets close to ten. For example, replacing an include with the provider’s actual IP addresses, in ip4 entries, removes a lookup entirely. Moreover, removing tools you no longer use, and dropping the a and mx mechanisms when your own servers never send mail, frees up room. In sum, keep the count under ten, keep the record to one line, and remember that only one SPF record may exist per domain: two SPF records also produce a permerror.
What SPF cannot do
SPF cannot prove an email was not changed, and it cannot protect the address your reader sees. A spammer who owns a domain can publish a perfect SPF record for it, pass SPF, and still forge your name in the From line. That is not a flaw in SPF. That is the job DMARC was built for. SPF also cannot survive forwarding, as the forwarded copy arrives from a different server. Knowing those limits is what makes a sender set up DKIM next, rather than assuming SPF alone is enough.
DKIM in depth: the wax seal on every email

In fact, DKIM, DomainKeys Identified Mail, signs every email with a private key and publishes the matching public key in DNS. For example, the sending server hashes the email’s headers and body, encrypts that hash with the private key, and attaches the result as a DKIM-Signature header. Similarly, the receiving server fetches the public key from DNS, decrypts the hash, and checks whether it matches the email it received. In short, a matching hash means the email arrived exactly as the sender wrote it.
Secondly, DKIM is the strongest of the three checks for a cold email sender, because it survives forwarding. In fact, forwarding changes the sending server, which breaks SPF, yet it usually leaves the email content untouched, so the DKIM signature still matches. For example, a forwarded email with a valid DKIM signature will pass DMARC through DKIM alignment even when SPF fails. Moreover, that is why the DMARC logic needs only one aligned pass: DKIM is the safety net. As a result, a sender who skips DKIM has no safety net at all.
SPF DKIM DMARC explained: how DKIM signing works
DKIM signing has three parts: a selector, a key pair, and a DNS record. Firstly, the selector is a short name, such as s1 or google, that tells the receiver which public key to fetch. For instance, the receiver looks up s1._domainkey.example.com to find the key for selector s1. Similarly, the private key stays secret on the sending server, while the public key is published in that DNS record for anyone to read. In sum, the selector is the label on the key, and the DNS record is where the public half lives.
In addition, the signature header itself carries the detail. Above all, the d= tag names the signing domain, the s= tag names the selector, and the h= tag lists which headers were signed. For example, a signature with d=example.com and s=s1 tells the receiver to fetch the key at s1._domainkey.example.com. Moreover, the bh= tag holds the hash of the body, so any change to the message text breaks the match. As a result, a DKIM failure usually means one of three things: the content changed in transit, the wrong key is published, or the selector in the signature does not match the record in DNS.
A DKIM record, and what each part means
s1._domainkey.example.com TXT "v=DKIM1; k=rsa; p=MIGfMA0GCSqGSIb3DQEBAQUAA4GNADCBiQKBgQC..."In fact, v=DKIM1 marks the record as DKIM version one. For example, k=rsa names the key type, which is RSA for almost every sender. Similarly, p= holds the public key itself, a long string of characters that the receiver uses to check the signature. Moreover, most sending tools generate this record for you, and the sender’s only job is to paste it into DNS exactly as given, without breaking the long key across lines or adding spaces. As a result, a pasted key with a stray space or a missing character is one of the most common DKIM failures, and also one of the easiest to fix.
Key length, and why 2048 bits is the right choice
DKIM keys come in lengths, and the length matters. A 1024-bit key is the minimum most providers still accept, yet it is short enough that security guidance has moved past it. A 2048-bit key is the standard choice today, and every major sending tool supports it. Some DNS providers limit a single TXT string to 255 characters, so a 2048-bit key must be split into two quoted strings in the record, which DNS joins back together. Check your DNS provider’s guidance before publishing a long key, and test the record with a free DKIM checker afterwards.
SPF DKIM DMARC explained: rotating DKIM keys
Keys should be rotated, which means replacing them on a schedule rather than waiting for a problem. Firstly, generate a new key pair under a new selector, such as s2, and publish the new public key in DNS. For instance, keep the old selector live while the new one propagates, which takes up to 48 hours. Similarly, switch the sending tool to sign with the new selector, watch the DMARC reports for a few days, and only then remove the old record. As a result, rotation never breaks a single email, because the old and new keys overlap. A yearly rotation is a sensible habit for most senders.
What DKIM cannot do
DKIM cannot say what should happen to an email that fails its check. A forged email with no signature at all simply has no DKIM result, and the inbox must decide what to do with it on other grounds. DKIM also cannot prove who sent the email, only that the holder of the private key signed it. Those two gaps are exactly what DMARC fills: a policy for failures, and a link between the signature and the address the reader sees.
DMARC in depth: the policy and the reports
In fact, DMARC, Domain-based Message Authentication, Reporting and Conformance, is the policy layer that sits on top of SPF and DKIM. For example, it tells a receiving inbox what to do when an email fails both checks, or fails alignment, and it asks the inbox to send you a report about it. Similarly, it is published as a TXT record at _dmarc.example.com, and it is the only one of the three checks that the reader never sees directly. In short, DMARC turns two silent checks into a decision and a paper trail.
Secondly, DMARC is the check that actually stops spoofing. In fact, SPF and DKIM can both pass for a spammer’s own domain while the visible From line shows your name. For example, DMARC catches that trick, because it asks whether the passing check lines up with the From address the reader sees. Moreover, when neither check aligns, DMARC applies your policy: deliver it, quarantine it, or reject it. As a result, DMARC is the reason a spammer cannot simply borrow your name, and the reason your own mail needs to pass alignment too.
SPF DKIM DMARC explained: the DMARC policy ladder
A DMARC record has three policies, and the safe path climbs them one step at a time. Firstly, p=none means the inbox delivers the email and sends you a report, which is the watching stage. For instance, a new sender should run p=none for one to two weeks while reading the reports. Similarly, p=quarantine means the inbox sends failing mail to spam, which is the testing stage. Moreover, p=reject means the inbox refuses failing mail outright, which is the finished stage. As a result, the ladder is none, then quarantine, then reject, and skipping a rung is how senders block their own mail.
| Policy | What happens to failing mail | When to use it |
|---|---|---|
| p=none | Delivered, and you get a report | First 1 to 2 weeks, while you learn who sends as you |
| p=quarantine | Sent to spam | After reports show your own mail passes cleanly |
| p=reject | Refused outright | Only when reports are clean at quarantine, and DKIM is strong |
The policy ladder above is the safe progression for every sender. Never jump straight to p=reject: a strict policy published before your own sending is fixed will block your own real emails. Last checked: 16 November 2026.
A DMARC record, and what each tag means
v=DMARC1; p=none; rua=mailto:dmarc@example.com; ruf=mailto:dmarc-forensic@example.com; pct=100; sp=quarantine; adkim=r; aspf=rIn fact, v=DMARC1 marks the record, and p= sets the policy for the domain. For example, rua= names the address that receives aggregate reports, the daily XML summaries of who sent mail as you and whether it passed. Similarly, ruf= names the address for forensic reports, the detailed copies of individual failures, which many large providers no longer send for privacy reasons. Moreover, pct= sets the percentage of failing mail the policy applies to, sp= sets the policy for subdomains, and adkim=r and aspf=r set relaxed alignment for DKIM and SPF. As a result, the record above is a sensible starting point: watch everything, quarantine subdomains, and keep alignment relaxed.
SPF DKIM DMARC explained: reading DMARC reports
Aggregate reports are the most valuable thing DMARC gives you, and they are also the most intimidating at first sight. Firstly, each report is an XML file, sent daily by every inbox provider that received mail from your domain. For instance, it lists every sending server, how many emails it sent, and whether SPF, DKIM and DMARC passed for each one. Similarly, a report reader turns that XML into a readable dashboard, so the sender does not have to read raw XML. Moreover, the first thing to look for is any server you do not recognise: that is either a tool you forgot about, or someone spoofing you. As a result, the reports are how a sender discovers the forgotten newsletter tool, the old CRM, and the attacker, all in the same week.
In addition, forensic reports are rarer and more detailed. Above all, they arrive per failed email, with the headers attached, so the sender can see exactly why one message failed. For example, a forensic report will show a DKIM failure caused by a mailing-list footer, or an SPF failure caused by a forwarder. Similarly, many large providers, including Gmail, do not send forensic reports at all, so the aggregate reports are the reliable source. In sum, read the aggregates every week, act on the surprises, and let the forensic reports fill in the detail when they arrive.
The pct tag, and how to use it as a safety valve
The pct tag applies the policy to only a percentage of failing mail, and it is the safety valve for a cautious rollout. A sender moving from p=none to p=quarantine can start at pct=25, watch the reports for a week, then raise it to 50, then 75, then 100. The same valve works for the move to p=reject. A sender who uses pct in steps will catch a misconfigured tool while it affects a quarter of the mail, not all of it. That is a far cheaper lesson than a full outage.
Subdomain policy, and the domains you never send from
The sp tag sets the policy for subdomains, and it deserves attention of its own. A subdomain such as mail.example.com inherits the main policy unless sp says otherwise, so a sender who sets p=none on the main domain and forgets sp leaves subdomains unprotected. Worse, a domain the sender never uses for email at all, such as a parked domain, has no SPF or DKIM, which makes it the easiest target for a spoofer. Publishing a DMARC record with p=reject on a non-sending domain, plus an SPF record of v=spf1 -all, tells every inbox to refuse all mail from it. That one record costs nothing and closes the easiest door a spoofer can use.
Setting up SPF, DKIM and DMARC, step by step
In fact, the setup order matters, and it is the same as the order in this guide: SPF first, then DKIM, then DMARC at p=none. For example, a sender who publishes DMARC first will watch it fail, because there is nothing underneath it yet. Similarly, a sender who publishes all three at once will not know which one is broken when the tests fail. Moreover, the whole job takes an afternoon for the records, plus about two weeks of watching reports before the policy tightens. As a result, the steps below are written to be followed in order, with a test after each one.
Step 1: list every tool that sends email for your domain
Before touching DNS, list every service that sends email as you. That list includes the sending tool, the mailbox provider, the CRM, the support desk, the invoicing tool, the website’s contact form, and the newsletter platform. A forgotten tool is the most common cause of a DMARC failure, because its servers are not on the SPF list and its signatures do not align. Walk through the business, ask each team what sends email, and write the list down. The DMARC reports will check your work later, yet starting from a complete list saves a week of surprises.
Step 2: publish the SPF record
Build one SPF record that covers every sender on the list, using includes for the tools that publish their own SPF and ip4 entries for fixed servers. Publish it as a TXT record on the domain root, with no other SPF record beside it. Wait up to 48 hours for DNS to spread, then test it with a free SPF checker. If the checker reports too many lookups, flatten the record by replacing an include with the provider’s IP addresses. Switch from ~all to -all only after your own mail passes.
Step 3: publish the DKIM record
Generate a DKIM key pair in each sending tool, using a 2048-bit key and a clear selector name, and publish the public key as a TXT record at selector._domainkey.yourdomain. Most tools show the exact record to paste, and the sender’s only job is to copy it without adding spaces or line breaks. Wait for DNS to spread, send a test email, and check the DKIM result in the headers. Repeat the step for every tool that sends as you, using a different selector for each one, so a key can be rotated for one tool without touching the others.
Step 4: publish DMARC at p=none, then watch the reports
Publish the DMARC record at _dmarc.yourdomain with p=none and a rua address that can receive the daily reports. A dedicated mailbox for DMARC reports is worth setting up, because the volume grows fast and the reports will flood a personal inbox. Read the reports for one to two weeks, add any forgotten sender to SPF or DKIM, and fix every alignment failure. Move to p=quarantine, first at a low pct, then raise it. Move to p=reject only when the reports are clean at quarantine and DKIM is strong, because reject with weak DKIM will block forwarded mail your readers expect.
Adding an SPF record in Google Workspace, on video
Video: How To Add An SPF Record To Your Domain With Google Workspace [2.2] by Emailchaser on YouTube. This video is the creator’s property, embedded via YouTube for education. OutreachCompare is not affiliated with Emailchaser and does not claim ownership of this video.
In fact, the video above shows the hands-on part of step two: adding an SPF record to a domain in Google Workspace. For instance, it walks through the DNS settings, where the TXT record goes, and how to check that it was added correctly. It is short, practical, and directly about cold email sending, because a wrong SPF record is the fastest way to land in spam. Watch it with your own DNS panel open, and follow along with your real domain.
How long each step takes
| Step | What you do | Time to publish | Time to trust it |
|---|---|---|---|
| 1. List senders | Write down every tool that sends as you | An hour | Checked by the first DMARC reports |
| 2. SPF | Publish one TXT record on the domain root | Minutes, plus DNS spread | Test the same day |
| 3. DKIM | Publish one TXT record per tool, per selector | Minutes per tool | Test with a real email the same day |
| 4. DMARC p=none | Publish the record, read reports for 1 to 2 weeks | Minutes | 1 to 2 weeks of reports |
| 5. Tighten policy | Quarantine, then reject, in pct steps | Minutes per step | A week per step |
The timetable above is realistic for a small sender with two or three tools. A larger sender with many tools should allow a month from p=none to p=reject, and should never rush the report-reading stage. Last checked: 16 November 2026.
Common errors and how to fix them
In fact, most authentication failures come from a small set of mistakes, and every one of them is fixable. For example, a record with a typo, a second SPF record, a selector that does not match, or a policy published too early will each break the system in a different way. Similarly, the fixes below are ordered by how often the error appears, starting with the one that catches out the most senders. As a result, a sender who works through this section with a checker open will fix almost any failure in an afternoon.
SPF DKIM DMARC explained: the seven most common errors
| Error | What you see | The fix |
|---|---|---|
| Too many DNS lookups | SPF permerror, check fails | Count lookups, flatten includes into ip4 entries, drop unused tools |
| Two SPF records | SPF permerror, check fails | Merge them into one TXT record; only one SPF record may exist |
| SPF record too long | Record truncated or rejected | Split the TXT value into quoted strings, or flatten includes |
| DKIM selector mismatch | DKIM fail, key not found | Check the s= tag matches the DNS name exactly, including case |
| DKIM key pasted wrong | DKIM fail, bad key | Re-paste the p= value exactly, with no spaces or line breaks |
| DMARC alignment failure | SPF and DKIM pass, DMARC fails | Align the envelope sender or the d= domain with the From domain |
| p=reject too early | Your own mail blocked | Drop back to p=quarantine or p=none, fix the cause, then climb again |
The seven errors above cover the failures most senders will ever see. Work through them with a free checker open, and fix one thing at a time, testing after each change. Last checked: 16 November 2026.
More errors, and how to fix them
| Error | What you see | The fix |
|---|---|---|
| No DMARC record | Inbox warnings, no reports | Publish _dmarc with p=none and a rua address today |
| DMARC record at wrong host | Record not found | Publish at _dmarc.yourdomain, not the domain root |
| Subdomain has no policy | Subdomain spoofed freely | Set sp=quarantine or sp=reject, or publish p=reject on unused domains |
| rua mailbox overflowing | Reports bouncing, inbox full | Use a dedicated mailbox or a report reader, and check it weekly |
| Third-party sender fails alignment | Their SPF and DKIM pass, DMARC fails | Ask the tool for custom DKIM signing on your domain |
| Forwarding breaks SPF | SPF fail on forwarded mail | Rely on DKIM alignment, and keep p=reject until DKIM is strong |
The second table covers the quieter failures: the missing record, the wrong host, and the third-party tool that never aligned. Each one is fixed in DNS or in the tool’s settings, never by guessing. Last checked: 16 November 2026. Features and pricing can change, so please check the provider’s site before you buy.
The “no DMARC record” warning, and why it appears now
Many senders first meet DMARC through a warning, not a failure. Gmail and Yahoo require bulk senders, those sending more than about 5,000 emails a day to their users, to publish SPF, DKIM and DMARC, keep spam complaint rates below 0.3%, and offer one-click unsubscribe. A sender with no DMARC record will see warnings in inbox provider tools and in deliverability checkers, and may see mail throttled. The fix is the same as the setup in this guide: publish DMARC at p=none today, read the reports, and climb the ladder. The warning is not a punishment. It is the inbox asking for proof.
When the error is not in DNS at all
Some failures look like DNS errors and are not. A sending tool that signs with its own domain instead of yours will pass DKIM yet fail alignment, and no DNS change will fix it: the fix is in the tool, by turning on custom DKIM signing for your domain. A tool that sends from a shared IP pool will pass SPF through its include, yet the shared pool’s reputation can still hurt delivery, and the fix is a dedicated IP or a different pool. A list that earns spam complaints will hurt delivery even with perfect authentication, and the fix is list hygiene, not DNS. Check the DNS first, then check the tool, then check the list.
How to check your setup
In fact, authentication is only real when it is tested, and testing is free. For example, a sender who publishes three records and never checks them may have a typo in one, a second SPF record beside the first, or a selector that does not match. Similarly, a sender who tests after every change will catch each mistake in minutes. Moreover, the checks below take less than an hour in total, and they should be repeated after every DNS change, every new tool, and every key rotation. As a result, testing is not a one-off chore. It is a habit.
Free checkers that cover all three records
| Checker | What it checks | Best for |
|---|---|---|
| MXToolbox | SPF, DKIM and DMARC records, plus lookups | A fast first check of every record at once |
| Google Admin Toolbox | SPF, DKIM and DMARC, with plain explanations | Senders on Google Workspace checking their own domain |
| Postmark DMARC check | SPF, DKIM and DMARC in one report | A readable pass or fail for all three, from Postmark |
| Mail-tester | A real email, scored out of 10 | Seeing what a receiving inbox actually sees |
The checkers above are free tools from their providers, linked by name so the reader can find them. Run at least two of them after every DNS change, because each one explains failures slightly differently. Last checked: 16 November 2026.
Reading the Authentication-Results header
The most honest test is a real email, read in its own headers. Send a test email to yourself, open the original message, and find the Authentication-Results header. It will show spf=pass or fail, dkim=pass or fail, and dmarc=pass or fail, each with the domain it checked. A pass on all three, with the domains matching your From address, means the setup works. A fail on one tells you exactly which record to fix. That header is the ground truth, and it beats any checker when the two disagree.
What a pass looks like, and what a fail looks like
A clean pass reads like this: spf=pass, dkim=pass, dmarc=pass, all three naming your domain. A common mixed result reads spf=pass, dkim=pass, dmarc=fail, which means the checks passed for the wrong domain and alignment is the problem. A worrying result reads spf=permerror, which means the SPF record itself is broken, usually by too many lookups or two records. A silent result, with no DMARC line at all, means no DMARC record exists. Each of those has a fix in the errors section above, and each one is worth checking with a real email rather than a guess.
A weekly routine that keeps authentication healthy
Set a weekly routine and authentication will never quietly break. Read the DMARC aggregate reports once a week, looking for new senders and new failures. Re-run the three checkers after any DNS change, any new tool, or any key rotation. Check the Authentication-Results header on a test email once a month. That routine takes under half an hour a week, and it catches the forgotten tool, the expired key, and the spoofing attempt before any of them becomes a deliverability problem. Our Deliverability Guide 2026 covers the wider routine, and our Inbox Placement Guide 2026 shows how to test whether emails are actually landing.
BIMI in brief: your logo in the inbox
In fact, BIMI, Brand Indicators for Message Identification, puts your logo beside your emails in the inbox. For example, a reader who sees your logo next to your name will trust the email more, and a spoofer who cannot show the logo will stand out. Similarly, BIMI is a TXT record at default._bimi.yourdomain that points at an SVG version of your logo. Moreover, it only works when DMARC is already at p=quarantine or p=reject, because the inbox will only show a logo for a domain it has already verified. As a result, BIMI is a reward for finishing DMARC properly, not a shortcut around it.
Secondly, BIMI has one extra requirement that surprises senders: a Verified Mark Certificate, a VMC, from a certificate authority, which proves the sender owns the trademark in the logo. For example, the certificate costs money and takes time to obtain, and not every inbox provider displays BIMI logos yet. In contrast, Gmail and Yahoo both support it, which covers most consumer inboxes. In sum, BIMI is worth doing for a sender with a real brand and a finished DMARC setup, and worth skipping until then. Mailgun supports BIMI on its platform, and its review covers the detail.
Tools that help with SPF, DKIM and DMARC
In fact, the tools below are compared on one question only: how well do they help with authentication? For example, a tool with DMARC monitoring will read the reports for you, while a tool with automated setup will publish the records for you. In contrast, a tool that only sends email will leave the DNS work to you. In short, the tables below list the prices exactly as the providers show them, checked on 16 November 2026, with “check the site” wherever a figure is not stated.
Secondly, the ranking is not by sending power. In fact, a high-volume sender with no monitoring ranks below a smaller tool that watches your authentication every day. Similarly, a dedicated IP server with automated SPF, DKIM and DMARC ranks above a shared pool that leaves the records to you. Moreover, the decision section after these tables turns the comparison into a pick, based on the sender’s situation. The help with authentication is the deciding factor in this section, not the email volume.
SPF DKIM DMARC explained: authentication-tool pricing, part one
| Tool | Plan priced | Price / month | Authentication help included |
|---|---|---|---|
| Postmark Visit Postmark → | Basic | $15 for 10,000 emails | DMARC monitoring from $14 a month a domain; managed IP warmup |
| Mailgun Visit Mailgun → | Basic | $15 for 10,000 emails | SPF, DKIM, DMARC and BIMI supported; automated IP warmup; Optimize price, check the site |
| Amazon SES Visit Amazon SES → | A la carte | $0.10 per 1,000 emails | SPF, DKIM and DMARC supported; dedicated IPs $24.95 a month standard |
| SendGrid Visit SendGrid → | Essentials | From $19.95 for 50,000 emails | SPF, DKIM and DMARC supported; dedicated IP and automated warm-up on Pro |
Authentication-tool pricing, part two
| Tool | Plan priced | Price / month | Authentication help included |
|---|---|---|---|
| Do You Mail Visit Do You Mail → | Server | $39 a server | Automated SPF, DKIM and DMARC; dedicated USA or EU IP; replacement IP $100 one-time if blacklisted |
| Smartlead Visit Smartlead → | Base | $39, or $32.50 annual | SmartDelivery from $49 a month; SmartServers $39 a server a month; warmup help, check the site for DMARC monitoring |
| Instantly Visit Instantly → | Growth | $47, or $37.60 annual | Custom tracking domains; unlimited warmup; no trial shown |
The prices above were read on the official sites on 16 November 2026. Do You Mail’s homepage also shows $40 a month in one scaling example, so confirm the $39 server price on the site. Mailgun Optimize pricing is not shown clearly, so the article says check the site rather than guessing. Last checked: 16 November 2026. Features and pricing can change, so please check the provider’s site before you buy. We do not guess at features, prices or trials.
What the next step up costs
The headline price is rarely the whole price for authentication help. Postmark’s Basic plan is $15 for 10,000 emails, yet DMARC monitoring is a separate $14 a month per domain, and a dedicated IP starts at $50 a month on Pro plans sending 300,000 or more a month. Mailgun’s Foundation plan is $35 for 50,000 emails and Scale is $90 for 100,000, with the Optimize deliverability suite priced separately, so check the site before buying. Amazon SES is the cheapest per email at $0.10 per 1,000, yet its dedicated IPs are $24.95 a month each, and its Essentials, Pro and Enterprise tiers change the per-thousand price. A sender should price the authentication help they actually want, not the cheapest plan on the page.
SPF DKIM DMARC explained: authentication features at a glance
| Tool | DMARC monitoring | Automated SPF / DKIM / DMARC | Dedicated IP | Automated warmup |
|---|---|---|---|---|
| Postmark | Yes, from $14 a month a domain | No, records published by you | Yes, from $50 a month | Yes, managed IP warmup |
| Mailgun | Yes, in Optimize, check the site | No, records published by you | Check the site | Yes, automated IP warmup |
| Amazon SES | No | No, records published by you | Yes, $24.95 a month standard | Check the site |
| SendGrid | Check the site | No, records published by you | Yes, on Pro from $89.95 a month | Yes, automated warm-up on Pro |
More authentication features at a glance
| Tool | DMARC monitoring | Automated SPF / DKIM / DMARC | Dedicated IP | Automated warmup |
|---|---|---|---|---|
| Do You Mail | Yes, automated setup includes it | Yes, automated SPF, DKIM and DMARC | Yes, dedicated USA or EU IP server | No, no warm-up included |
| Smartlead | Check the site | No, records published by you | Yes, SmartServers $39 a server a month | Yes, premium Warmup Pool $59 a month on Base and Pro |
| Instantly | Check the site | No, records published by you | Check the site | Yes, unlimited warmup |
Feature details above were read on the official sites on 16 November 2026. “Check the site” means the provider’s page does not state the detail clearly, so confirm it before buying. Last checked: 16 November 2026. Features and pricing can change, so please check the provider’s site before you buy. We do not guess at features, prices or trials.
SPF DKIM DMARC explained: the honest pros and cons
Authentication has real strengths. Firstly, it proves your emails are really from you, which is the single biggest trust signal an inbox can receive. For example, a domain with all three checks passing will see better inbox placement than the same mail from an unauthenticated domain. Similarly, DMARC reports show you who is sending as you, including the attackers you never knew about. Moreover, BIMI becomes possible, and your logo can appear beside your name. Overall, the case for authentication is trust, visibility and protection.
In contrast, authentication has real costs too. In fact, it takes an afternoon to set up and about two weeks to tighten safely, and a mistake can block your own mail. For example, a strict DMARC policy published too early will refuse real emails, and a broken SPF record will fail every check. Similarly, the reports arrive daily and need reading, or they pile up unread. As a result, the honest rule is to go slowly, test after every change, and let the reports guide the policy. The work is real, yet the protection is worth it.
Who should do what: the decision framework
Let the situation pick the tool, not the feature list. In contrast, a sender with one domain and one tool needs a checker and a p=none record, not a monitoring subscription. For example, a sender with five tools and three domains needs monitoring, or the reports will drown them. Similarly, a sender who wants the DNS handled for them needs a server product, not a sending API. As a result, the framework below starts from the situation, and the right row usually picks itself. Start from the situation, and SPF DKIM DMARC explained becomes a simple choice.
Pick the authentication help that matches your situation
| Your situation | Pick this | Why |
|---|---|---|
| One domain, one sending tool | Free checkers + p=none | MXToolbox and a test email cover everything, at no cost |
| Want DMARC reports read for you | Postmark | DMARC monitoring from $14 a month a domain, Basic from $15 |
| High volume, needs deliverability suite | Mailgun | Optimize with placement tests and monitoring, from $15 a month |
| Cheapest per email, developer-led | Amazon SES | $0.10 per 1,000 emails, dedicated IPs $24.95 a month |
| Want the DNS handled for you | Do You Mail | Automated SPF, DKIM and DMARC on a dedicated IP, $39 a server a month |
| Agency sending, needs warmup too | Smartlead | SmartDelivery and SmartServers, from $32.50 a month annual |
| High-volume cold email, custom domains | Instantly | Custom tracking domains and unlimited warmup, from $37.60 a month annual |
That framework starts from the situation, not the feature list, so pick the row that matches your setup, then check the price on the provider’s own site before you buy. Last checked: 16 November 2026.
Ask three questions before spending anything
Three questions belong before a single dollar moves. In sum, the first is scale: how many domains and tools send as you, one, or ten? A single domain needs a checker, while ten domains need monitoring. Second, who does the DNS: you, your developer, or nobody at all? A sender with nobody to run DNS should pick a product that automates it. Finally, how much mail do you send: a few thousand a month, or hundreds of thousands? A small sender should pick the cheapest per-email option, while a large sender should pick the tool with the best monitoring. Answer those three, and the table above will point at one row.
A small sender with one domain should publish the three records by hand, read the free reports, and spend nothing. Firstly, a growing sender with several tools should pick Postmark DMARC monitoring at $14 a month a domain, and keep the sending where it is. A sender who wants the whole DNS job handled should pick Do You Mail at $39 a server a month, and accept that it has no sequences or warmup. Read our Postmark Review 2026, our Mailgun Review 2026, and our Amazon SES Review 2026 for the full picture on each one.
Frequently asked questions
SPF DKIM DMARC explained: do I need all three?
Yes, all three, because each one covers a blind spot the others leave open. SPF lists the allowed senders, DKIM proves the email was not changed, and DMARC links both checks to the address your reader sees and sets the policy for failures. A sender with only SPF can still be spoofed in the visible From line, and a sender with only DKIM has no policy for unsigned mail. Publish SPF first, then DKIM, then DMARC at p=none, and climb the policy ladder from there.
SPF DKIM DMARC explained: how long does setup take?
Publishing the records takes an afternoon, and trusting them takes about two weeks. DNS changes spread within 48 hours, and each record can be tested the same day it is published. DMARC at p=none then needs one to two weeks of reports before the policy moves to quarantine, and another week per step before reject. A sender who rushes to reject in a day risks blocking their own real mail, so the two-week wait is part of the job, not a delay.
SPF DKIM DMARC explained: what happens if I get p=reject wrong?
Receiving inboxes will refuse emails that fail DMARC, including your own real emails if they are misconfigured. The fix is to drop the policy back to p=quarantine or p=none at once, find the cause in the reports, fix the SPF list or the DKIM alignment, and climb the ladder again slowly. That is why the pct tag exists: it limits a new policy to a percentage of mail, so a mistake affects a quarter of the volume instead of all of it.
SPF DKIM DMARC explained: can I use one SPF record for many tools?
Yes, with one record that includes every tool, yet the 10-lookup limit is the constraint. Each include counts toward the limit, and the total must stay under ten DNS lookups, or the check returns a permerror and fails. Count the lookups with a free SPF checker, flatten includes into ip4 entries where you can, and remove tools you no longer use. Only one SPF record may exist per domain, so merge tools into a single record rather than publishing a second one.
SPF DKIM DMARC explained: does authentication stop all spam?
No, and it is important to be honest about that. Authentication proves an email really came from the domain it claims, and it stops spoofing of that domain, yet it says nothing about whether the email is wanted, useful, or well written. A spammer can authenticate their own domain perfectly and still send spam. Authentication is the foundation of deliverability, not the whole building: list quality, sending volume, warmup and content all matter too, as our Deliverability Guide 2026 explains.
SPF DKIM DMARC explained: which tool is best overall?
Postmark is the best overall pick for authentication help, because its DMARC monitoring reads the reports for you from $14 a month per domain, on top of a Basic plan from $15 for 10,000 emails. Mailgun is the best pick for a full deliverability suite, with Optimize, automated warmup and BIMI support from $15 a month. Do You Mail is the best pick for hands-off setup, with automated SPF, DKIM and DMARC on a dedicated IP server for $39 a month. We have not hands-on tested these tools ourselves, so there are no numeric scores here, only the verified prices and the honest trade-offs above.
The verdict
The verdict
SPF DKIM DMARC explained comes down to three habits: publish one SPF record that lists every sender, sign every email with DKIM on a 2048-bit key, and publish DMARC at p=none so the reports can teach you who sends as you. Climb the policy ladder slowly, none, then quarantine, then reject, in pct steps, and test after every change with a free checker and a real email. Read the aggregate reports every week, fix the surprises, and rotate your DKIM keys once a year.
Best for DMARC monitoring: Postmark, from $14 a month per domain, with Basic from $15 for 10,000 emails. Strongest for a full deliverability suite: Mailgun, from $15 a month, with Optimize, automated warmup and BIMI support. Top choice for hands-off setup: Do You Mail, with automated SPF, DKIM and DMARC on a dedicated IP server for $39 a month. We have not hands-on tested these tools ourselves, so there are no numeric scores here, only the verified prices and the honest trade-offs above.
Three moves to make today
Make three moves today. Moreover, list every tool that sends email as you, and check whether each one is on your SPF record. Next, publish a DMARC record at p=none with a rua address you will actually read, and send yourself a test email to check the Authentication-Results header. Then read the first aggregate report when it arrives, and add any forgotten sender to the list. Those three moves take less than a day, and they hand the sender everything needed to prove their emails are really theirs.
Keep the tools in perspective: they watch the records, they never replace the records. Similarly, the completeness of the SPF list, the strength of the DKIM key, and the patience of the DMARC rollout matter far more than any feature table. A sender who gets those three right will see their mail trusted on any tool in this guide. A complete list, a strong key, and a patient policy are SPF DKIM DMARC explained at their best. That is the honest truth behind every table above. Our Best Cold Email Tools for Developers 2026 guide ranks the same tools for a developer-led team, and our Cold Email Sequencing Guide 2026 shows how authentication fits into the wider sending system.
Keep reading
- How to Set Up a Sending Domain 2026, SPF, DKIM, DMARC and warmup, the full sending-domain setup
- How to Warm Up a New Email Domain 2026, warming up before the first send, so authenticated mail lands
- Inbox Placement Guide 2026, testing whether authenticated emails reach the inbox
- Deliverability Guide 2026, the wider deliverability picture behind every check
- How to Handle Cold Email Replies 2026, what to do once authenticated mail earns replies
- Cold Email Sequencing Guide 2026, how sequences and authentication fit together
- Best Cold Email Tools for Developers 2026, the same tools, ranked for a developer-led team
- Postmark Review 2026, the DMARC monitoring pick, reviewed in full
- Mailgun Review 2026, the deliverability suite pick, reviewed in full
- Amazon SES Review 2026, the cheapest per-email pick, reviewed in full